Pentera Logo Pentera Logo White
resources
Oct 2026
PHP2Shell: the expiry date on “too hard to exploit”
On 21 October 2026, PHP shipped emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619,...
Read now
“Pentera helps us prioritize what truly matters and gives us confidence we are covering our global environment continuously.”
“Seeing a domain admin account cracked in production changed how we view internal exposure.”
“Pentera helped us advance our red team and continuously improve penetration testing.”
“Pentera makes it easier to focus on what is truly exploitable instead of chasing long vulnerability lists.”
“In a complex, large-scale environment, Pentera delivers the speed and visibility security teams need.”
“Pentera amplified our team’s performance and delivered measurable value to upper management.”
"Pentera allows us to tailor testing to each service, reduce time and costs, and shift our focus from simply finding vulnerabilities to actively helping our teams fix them.”
Rubén Alonso | Head of Secure
Development Unit, Telefonica

“I don’t think we’d be able to advance our red team without Pentera. If you’re looking to improve penetration testing, I would definitely recommend it.”
Owen Fuller | Cybersecurity Engineering
Manager, Casey’s

Featured resources
Research
Oct 2026
PHP2Shell: the expiry date on “too hard to exploit”
Learn more
Featured resources
Datasheets
Sep 2026
Protect Patient Care with Continuous Security Validation
Learn more
Featured resources
Datasheets
Sep 2026
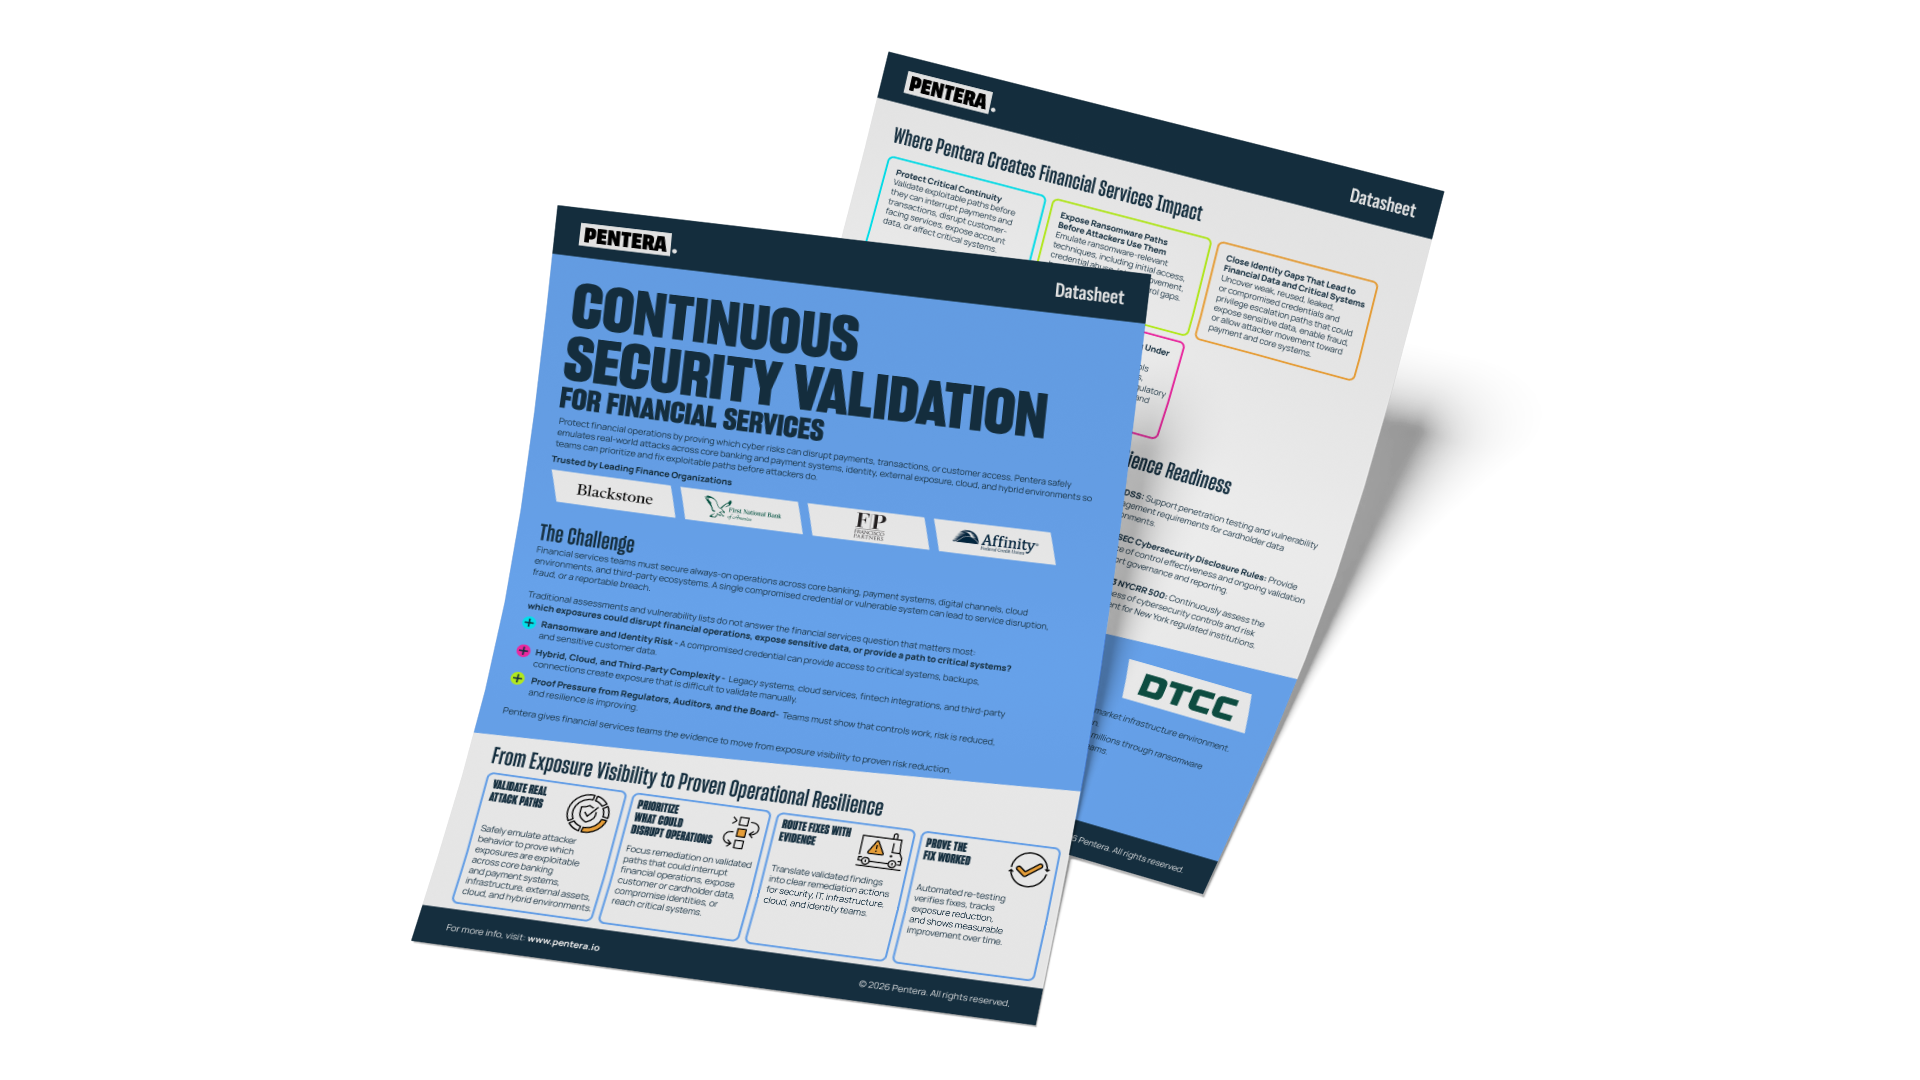
Continuous Security Validation for Financial Services
Learn more
1 / 3

Resources

Content Types
  • Cybertoons
Podcasts
Jan 2025
Compromised Credentials & Active Directories. Jeff Morrison, Pentera
Read more
Customer stories
Jan 2025
HiBank Case Study: Strengthening Cybersecurity with Automated Security Validation
Read more
Customer stories
Jan 2025
How HiBank Strengthened Continuous Security Validation Without Operational Disruption
HiBank Indonesia moved from periodic, consultant-led penetration tests to continuous, automated security validation with Pentera, eliminating long gaps in coverage. The platform enables frequent testing across on-prem and cloud environments without disrupting critical banking operations, while prioritizing vulnerabilities based on risk. As a result, the bank has improved remediation KPIs, systematically reduced exposure, and gained greater confidence in its overall security posture.
Read more
Research
Jan 2025
Blurring Boundaries: Risks of AWS SSM in Hybrid Landscapes
Read more
Podcasts
Dec 2024
Why Cloud Security Isn’t Perfect. (Hebrew)
Read more
Customer stories
Dec 2024
How Telefónica Improves Efficiency and Security Validation Across Services
Telefónica uses Pentera to improve efficiency, reduce costs, and validate vulnerabilities across a wide range of services. By shifting from manual pentesting to continuous validation, the team accelerates analysis and focuses on remediation instead of discovery.
Read more
Webinars
Dec 2024
Maximizing Impact: A Guide to Scaling Red Team Operations
Red teaming shouldn’t be limited to an annual exercise it should be a scalable, continuous program that measures real exposure. This webinar explains how automation can augment human expertise, safely emulate real attacker behavior, and accelerate testing across perimeter, phishing, Active Directory, and ransomware scenarios. By shifting from point-in-time assessments to ongoing validation, organizations can reduce dwell time, prioritize remediation, and maximize the impact of their security operations.
Read more
Webinars
Dec 2024
Navigare la conformità DORA e NIS2 con Pentera
Read more
Webinars
Dec 2024
Mettere alla prova la sicurezza nel cloud
Read more
Datasheets
Dec 2024
Achieve PCI DSS compliance with Automated Security Validation
Read more
Whitepapers
Dec 2024
A Guide to Achieving CAF Readiness
Read more
Webinars
Dec 2024
Cyber Attack Explained: Zero-Days in FortiClient VPN
A gut feeling led researchers to investigate Windows named pipes and uncover two vulnerabilities. The session explains how permissive permissions and elevated services enabled local privilege escalation, how configuration restore features could be abused for stealthy tampering and persistence, and closes with mitigations and lessons for defenders.
Read more