Pentera Logo Pentera Logo White
resources
Aug 2026
The Value Problem: What AI cannot decide for us
Pentera Labs Deep Dive - Part 4
Read now
“Pentera helps us prioritize what truly matters and gives us confidence we are covering our global environment continuously.”
“Seeing a domain admin account cracked in production changed how we view internal exposure.”
“Pentera helped us advance our red team and continuously improve penetration testing.”
“Pentera makes it easier to focus on what is truly exploitable instead of chasing long vulnerability lists.”
“In a complex, large-scale environment, Pentera delivers the speed and visibility security teams need.”
“Pentera amplified our team’s performance and delivered measurable value to upper management.”
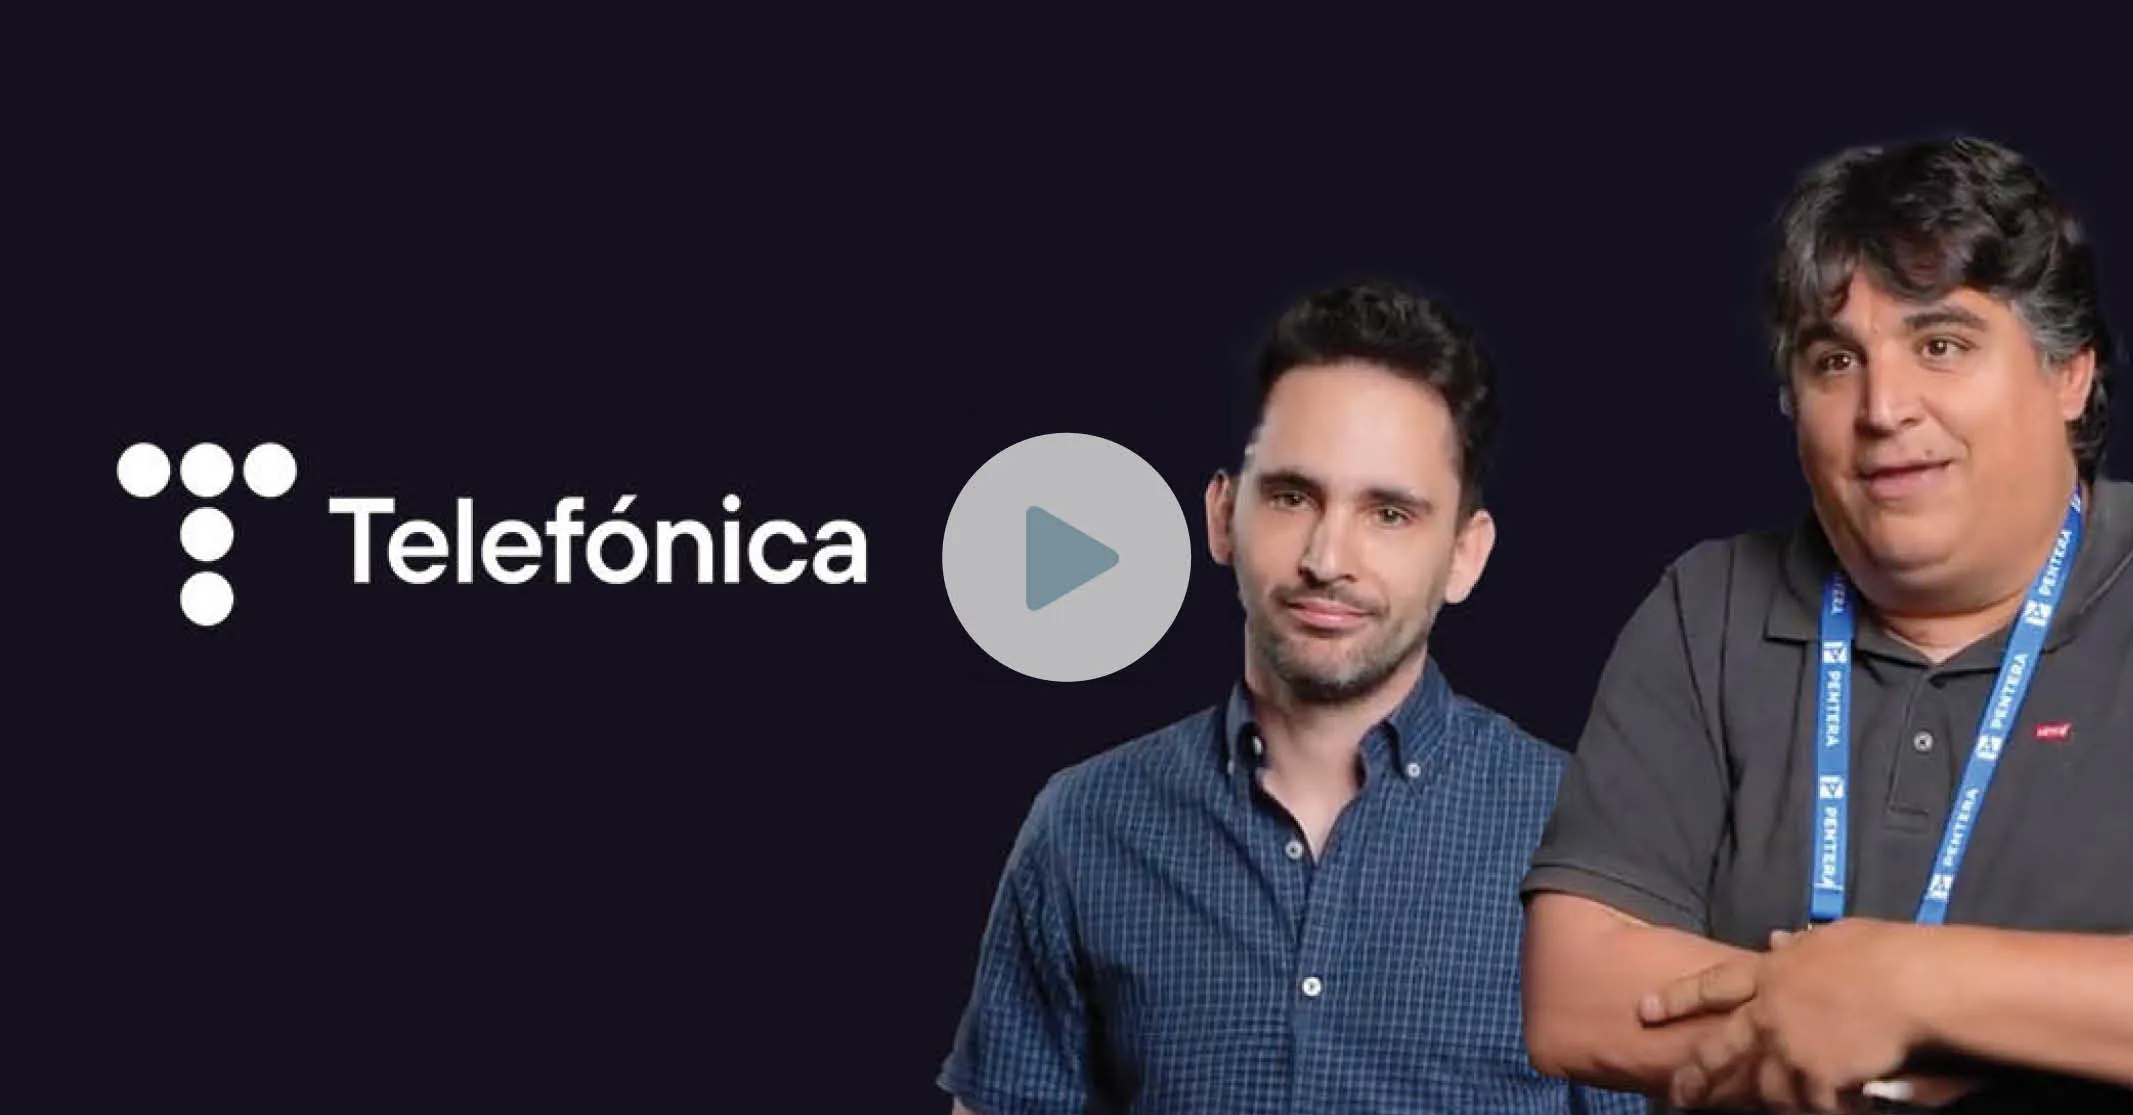
"Pentera allows us to tailor testing to each service, reduce time and costs, and shift our focus from simply finding vulnerabilities to actively helping our teams fix them.”
Rubén Alonso | Head of Secure
Development Unit, Telefonica

“I don’t think we’d be able to advance our red team without Pentera. If you’re looking to improve penetration testing, I would definitely recommend it.”
Owen Fuller | Cybersecurity Engineering
Manager, Casey’s

Pentera Solutions / Use Cases

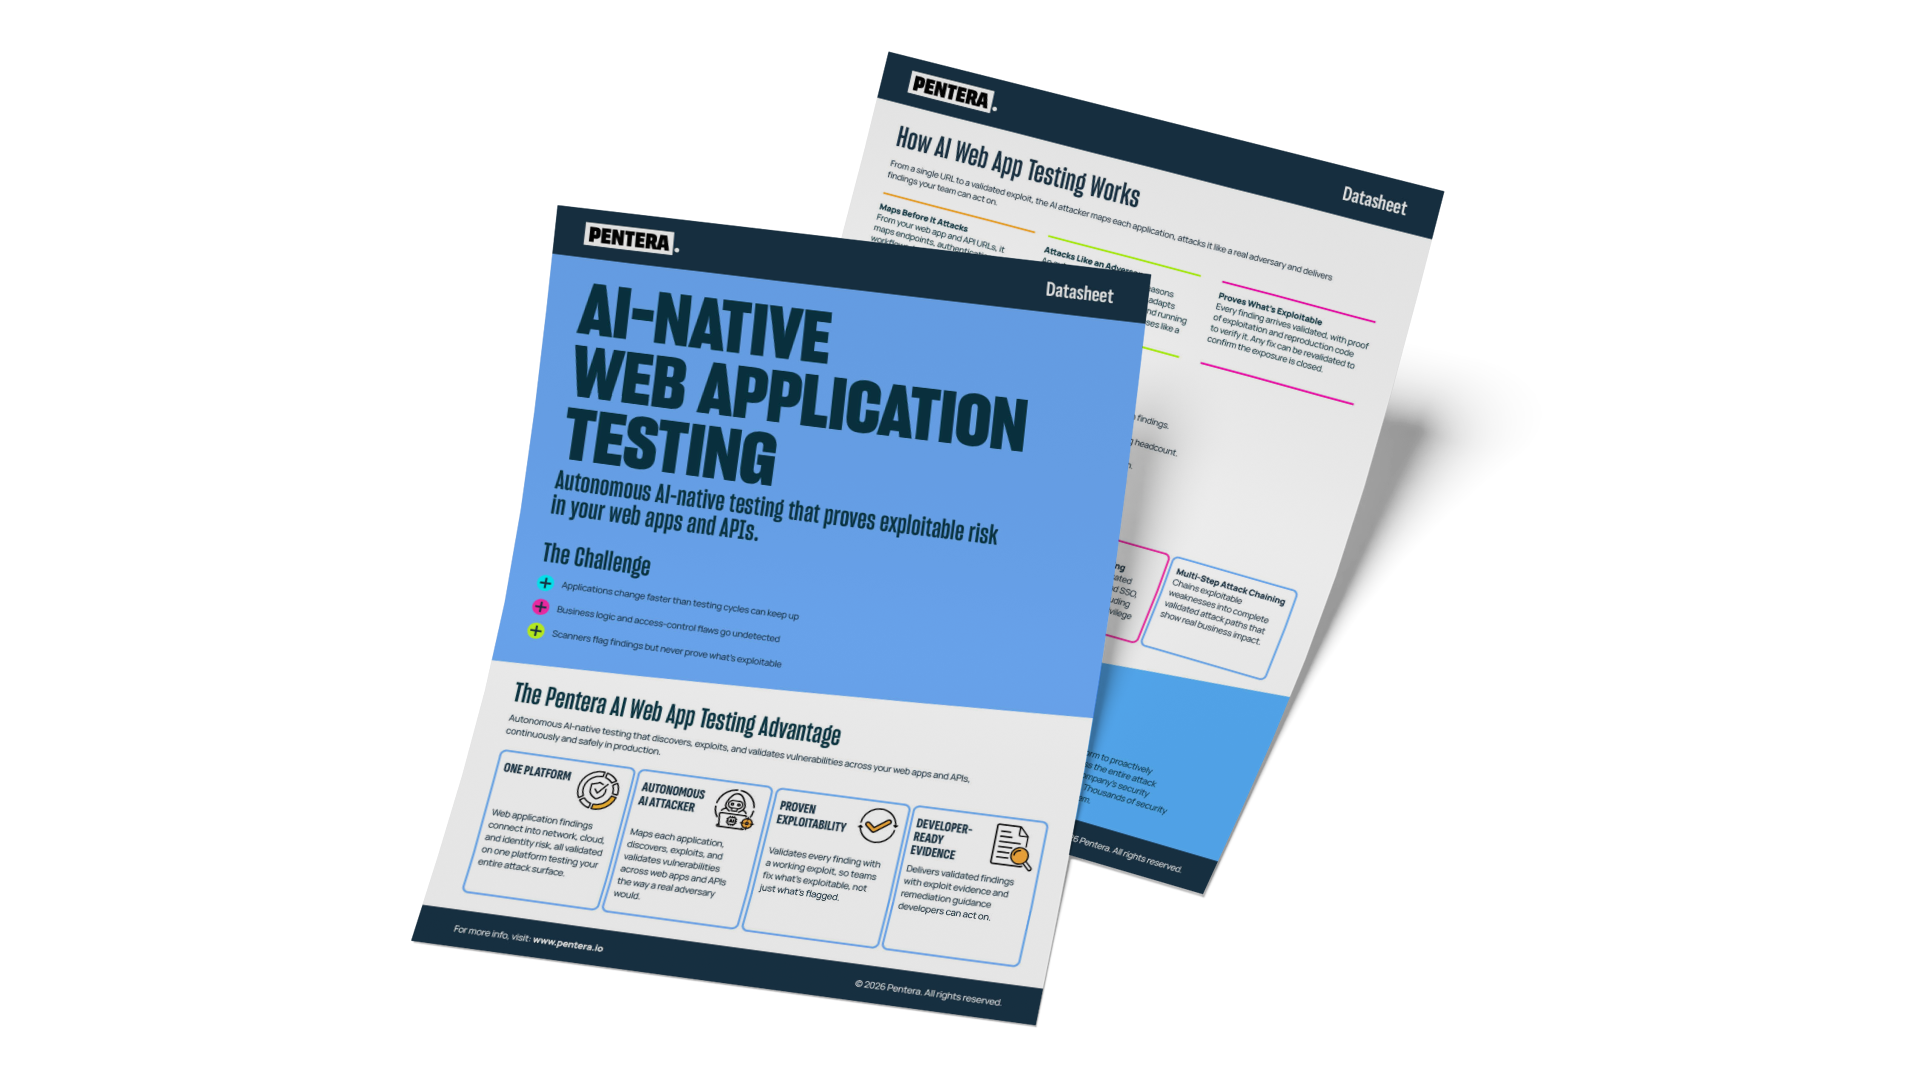
AI-Native Web Application Testing

Continuously validate exploitable risk across your web applications and APIs.
Put your web applications and APIs to the test against Pentera's autonomous AI attacker. It reasons through business logic and access controls like a real attacker, then proves what's exploitable. Pentera's Web App Testing provides evidence your teams can act on without slowing down your release cadence. Continuously validate exploitable risk across your web applications and apis.
Scanners flag findings, Pentera proves what's exploitable.
Thanks for reaching out! We'll be in touch soon to set up your personalized demo - prepare to unlock security insights about your environment!
TRUSTED CUSTOMERS
Why AI-Native Web Application Testing?

Prove and reduce real web application risk

Continuously test your web apps and apis, validate exploitable risk with deterministic execution, and prove exposure reduction over time.
AI That Thinks Like an Attacker

Map applications, reason through logic, adapt payloads in real time, and chain weaknesses into complete attack paths. Results are deterministic, reproducible, and auditable.

Prove What’s Actually Exploitable

Cut through scanner noise and alert fatigue. Confirm every finding with evidence. Prioritize remediation of proven risk, not potential flags.

Keep Pace With Application Change

Test continuously as your applications and APIs evolve, without adding headcount or waiting for the next manual pentest.

Validate Beyond the Application

Chain application flaws through your network, cloud, and identity to see the complete attack path.

Move From Find to Fix Faster

Equip developers with proof of exploitation and remediation steps. Retest to confirm fixes are closed.

Safety by Design

Run confidently in production with deterministic execution

Autonomous web app testing harnesses AI through customer-defined boundaries. Every action is governed by architectural controls, not prompt-level filters. Deterministic execution ensures every test is controlled, repeatable, and auditable. No maintenance windows, proven across 1,300+ customer environments over 10 years.

How it works

From target URL to validated risk

Start with a web application or api url and define the permitted scope. Pentera maps the application, adapts its attack, validates exploitable weaknesses, and provides the evidence needed to remediate them.
  • 1. Configure
  • 2. Set the Scope
  • 3. Run the Test
  • 4. Act on the Results
  • 5. Report the Impact
1. Configure
Choose your targets

Enter one or more web application or API URLs to begin testing.

2. Set the Scope
Define the testing boundaries

Set the permitted targets, access permissions, and safety guardrails. Add credentials, tokens, or session details for testing behind SSO, MFA, and OAuth.

3. Run the Test
Attack like an adversary

The AI attacker maps the application, reasons through its logic, adapts payloads, and chains exploitable weaknesses to demonstrate their impact.

4. Act on the Results
Review findings with exploit evidence, reproduction steps, and remediation guidance. Retest fixes to confirm the exposure is closed.
Move from validation to remediation
5. Report the Impact
Turn results into actionable insights

Generate executive and technical reports that communicate proven risk, business impact, and remediation progress.

AI-Native Web Application Testing Use Cases

Go beyond baseline web application testing

Pentera's AI attacker reasons through application logic, tests authenticated workflows, adapts attacks in real time, and chains weaknesses to prove what attackers can actually achieve. Coverage includes the owasp top 10 and goes deeper.

Full Application and API Discovery

Map modern web applications, client-side routes, hidden parameters, and undocumented REST, GraphQL, and WebSocket endpoints. Discover the complete attack surface before attackers do.

Authenticated Application Testing

Test applications behind SSO, MFA, and OAuth to identify exploitable weaknesses in session handling, token validation, account boundaries, and privilege transitions.

Business Logic and Access Control Testing

Reason through application workflows to uncover broken access control, IDOR, BOLA, cross-tenant access, unauthorized actions, and privilege escalation.

API and Injection Testing

Validate exploitable API and input-based weaknesses, including mass assignment, excessive data exposure, SQL injection, command injection, SSRF, insecure deserialization, and XSS.

AI and Supply Chain Testing

Assess third-party components and application-integrated AI for exploitable vulnerabilities, prompt injection, agent and tool abuse, data leakage, and exposed model endpoints.

End-to-End Attack Path Validation

Chain application weaknesses across network, cloud, and identity environments. Capture evidence of proven impact. Retest after remediation to verify the exposure is closed.
Pentera vs. the Alternatives

A different approach to web application testing

Capability
Frequency
Coverage
Scalability
Exploitability
Remediation
Pentera
Continuous, every release
Web app, network, cloud, identity
Scales across apps and attack surfaces
Deterministic validation with exploit evidence
Developer-ready evidence, targeted retest
AI Web Testing Tools
Varies by product and service tier
Primarily application focused
Limited to a single testing category
Validation methods vary by product
Remediation depth varies by product
Traditional DAST/Scanners
Scheduled scans
Surface-level, signature-based
Scales, but noisy
Potential findings, limited exploit proof
Severity score only
Manual Pentesting
Annual or periodic
Limited to engagement scope
Limited by consultant availability
Human-validated, point-in-time
Static report, manual follow-up

Frequently asked questions

AI web application testing is dynamic, attacker-led testing that maps an application’s endpoints, authentication, workflows, and logic, then selects and adapts attack techniques in real time. Deterministic tools confirm the result, so every finding is backed by evidence rather than an AI assumption. It is not static source-code analysis, and it is not a vulnerability scanner.

Yes. The OWASP Top 10 is the baseline, not the limit of Pentera’s testing. Pentera’s AI Web Application pentesting goes beyond known vulnerability patterns to reason through application logic, authenticated workflows, and access controls, adapting its attacks to uncover and prove exploitable risk that standardized testing can miss.

Vulnerability scanners flag potential weaknesses by signature and leave your team to determine which are real. Pentera instead acts like an attacker, discovering exposed applications, gaining authenticated access, chaining flaws together, and safely proving exploitation with evidence your team can act on.

Pentera combines AI-driven reasoning with deterministic validation to produce controlled, repeatable, and auditable results. It also connects web application findings to network, cloud, and identity on the same platform, allowing teams to understand risk beyond the application itself.

Yes. AI-Native Web Application Testing runs within customer-defined targets, access, and guardrails, with a complete audit trail of every action. Testing remains bound to the scope you approve.

Yes. Where an attack path continues beyond the application, so does Pentera, extending from the application into infrastructure, cloud, and identity within the scope you define. This shows the full path an adversary could take, not just the initial application flaw.

No. DAST and scanners flag potential weaknesses by signature; Pentera executes real attacks and validates exploitability with proof. SAST finds code issues early but cannot prove runtime exploitability; Pentera catches logic flaws and access control issues SAST misses. Manual pentesting applies deep reasoning but runs point-in-time; Pentera runs continuously, combining pentest-level depth with modern release frequency. Where scanners produce noise, Pentera produces proof.