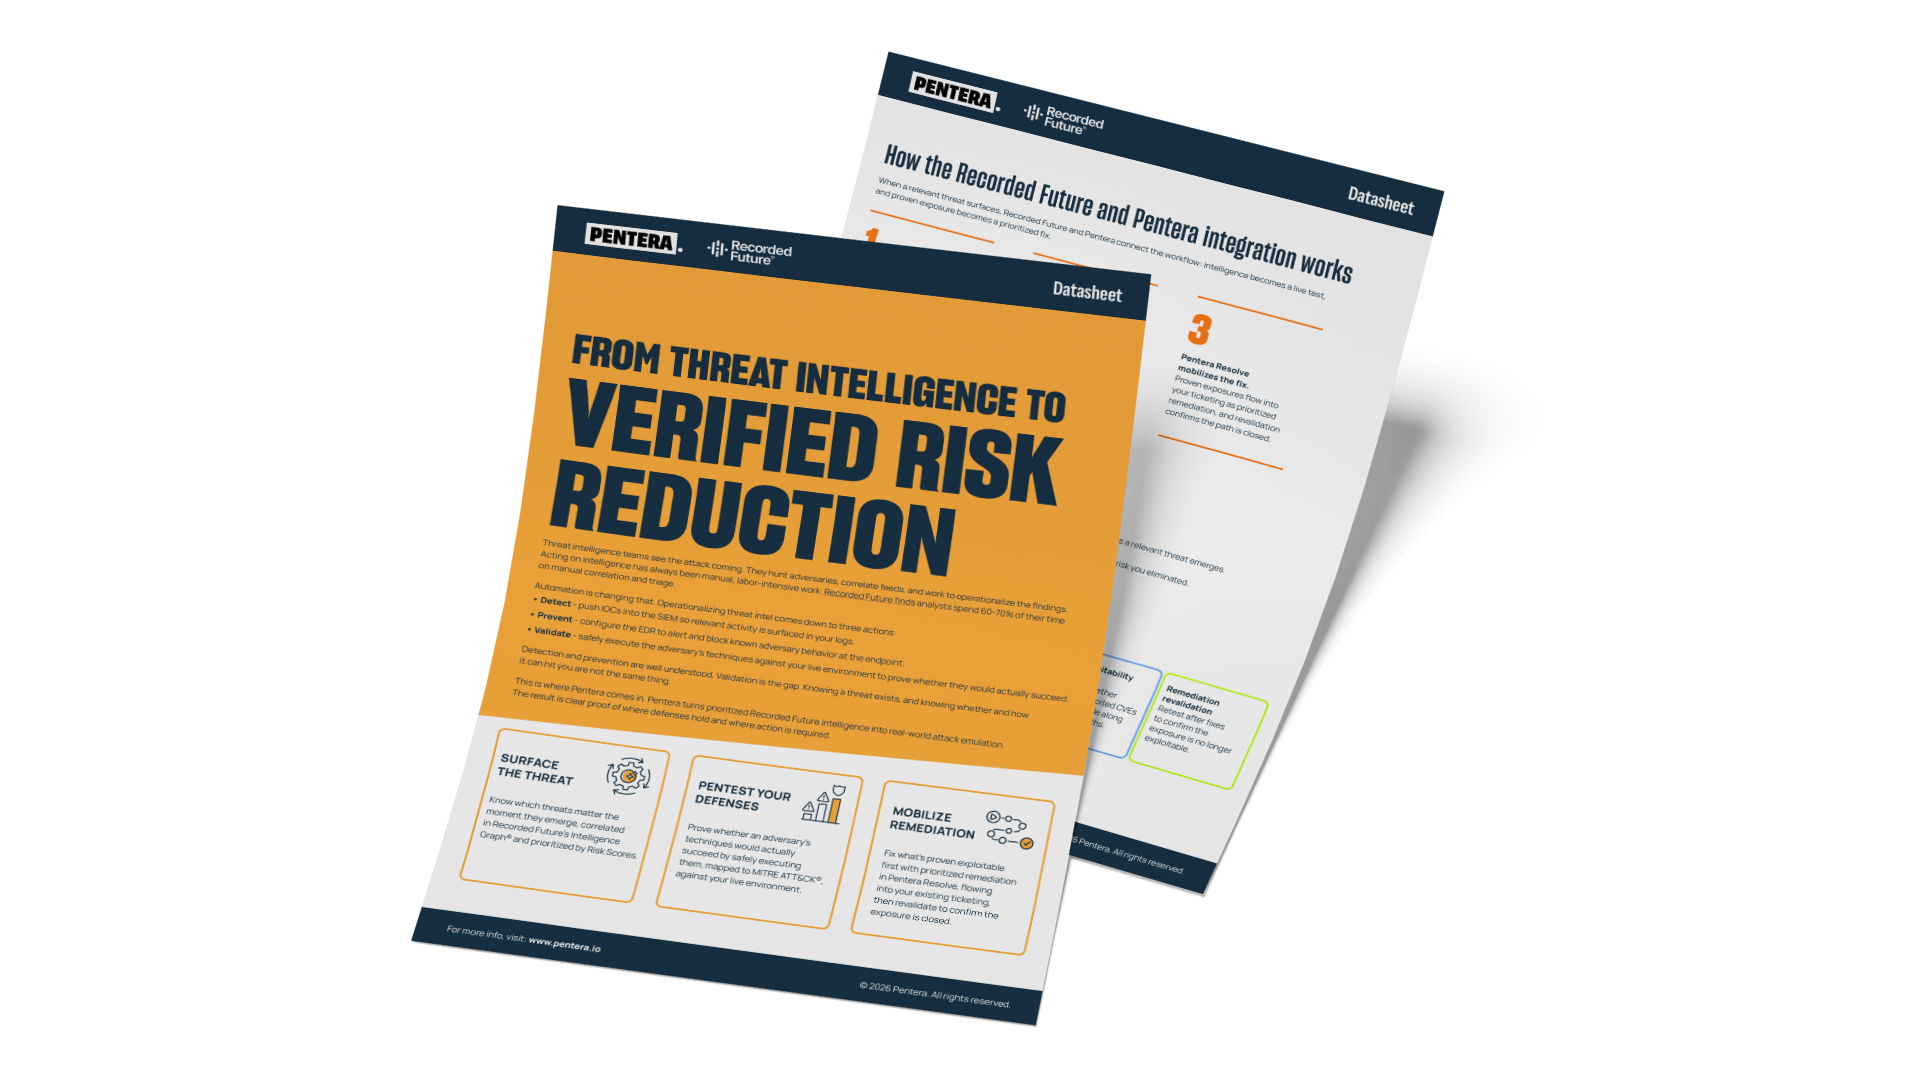
Proactively validate relevant threats as they emerge, and know which ones matter for your environment. Using Pentera’s AI-driven exposure validation extends security testing across every attack surface, at attacker speed, and turns the feed of threat intelligence into measurable risk reduction.
Validate relevant threats as they emerge instead of waiting for the next testing cycle. Keep testing aligned with a threat intelligence landscape that changes continuously.
Expand how much threat intelligence your organization can put to the test. AI-driven automation removes the dependency on manual research, scoping, and execution for every validation.
Test the threats surfaced by your intelligence against your tech environment. See where your defenses hold, where they fail, and which exposures require action.
Follow threats wherever they lead: from exposed assets and compromised identities to internal networks and cloud environments. Understand how the specific threats could impact your organization.
Move validated risk directly into natively integrated remediation workflows, so teams spend their time fixing exposures demonstrated to matter rather than working through another backlog of findings.
Retest after remediation to verify that fixes work and exposure is no longer exploitable, creating a measurable path from threat intelligence to risk reduction.
Deliver clear reporting on which threats were exploitable, what was fixed, and the risk your team eliminated.
Select a threat actor, campaign, adversary technique, actively exploited vulnerability, or compromised credential surfaced by a supported threat intelligence source.
Identify the assets, identities, and attack surfaces the threat may affect. Set the approved targets, access, and testing boundaries.
Pentera safely executes a focused adversarial test mapped to MITRE ATT&CK® and provides evidence of any exploitable exposure or attack paths.
Route validated exposure into owned remediation workflows with Pentera Resolve. Rerun the test after the fix to confirm the exposure is closed.
Pentera uses current threat intelligence to guide focused adversarial testing. Instead of following a checklist, it validates whether specific threats, vulnerabilities, credentials, and attacker techniques can succeed in your environment.
Pentera takes a signal from a supported threat intelligence source and translates it into a targeted test. It identifies the assets and identities that may be affected, safely validates exploitability, and provides evidence teams can use to prioritize remediation.
Pentera is designed to validate intelligence related to compromised credentials, threat actors, adversary techniques, actively exploited vulnerabilities, and campaigns.
Yes. Pentera executes every test under customer-controlled guardrails, including scoped access, throttling, and emergency stop controls, so validating a live threat doesn’t risk business disruption.
Traditional TLPT is typically delivered as a scheduled engagement. Pentera enables focused and repeatable validation when new threat intelligence requires action, helping teams assess exposure without waiting for the next manual testing cycle.
DORA and TIBER-EU define formal threat-led testing exercises with prescribed roles, scope, methodology, reporting, and remediation requirements. Pentera complements these engagements by helping teams validate threats, prioritize proven exposure, and test fixes between formal exercises.