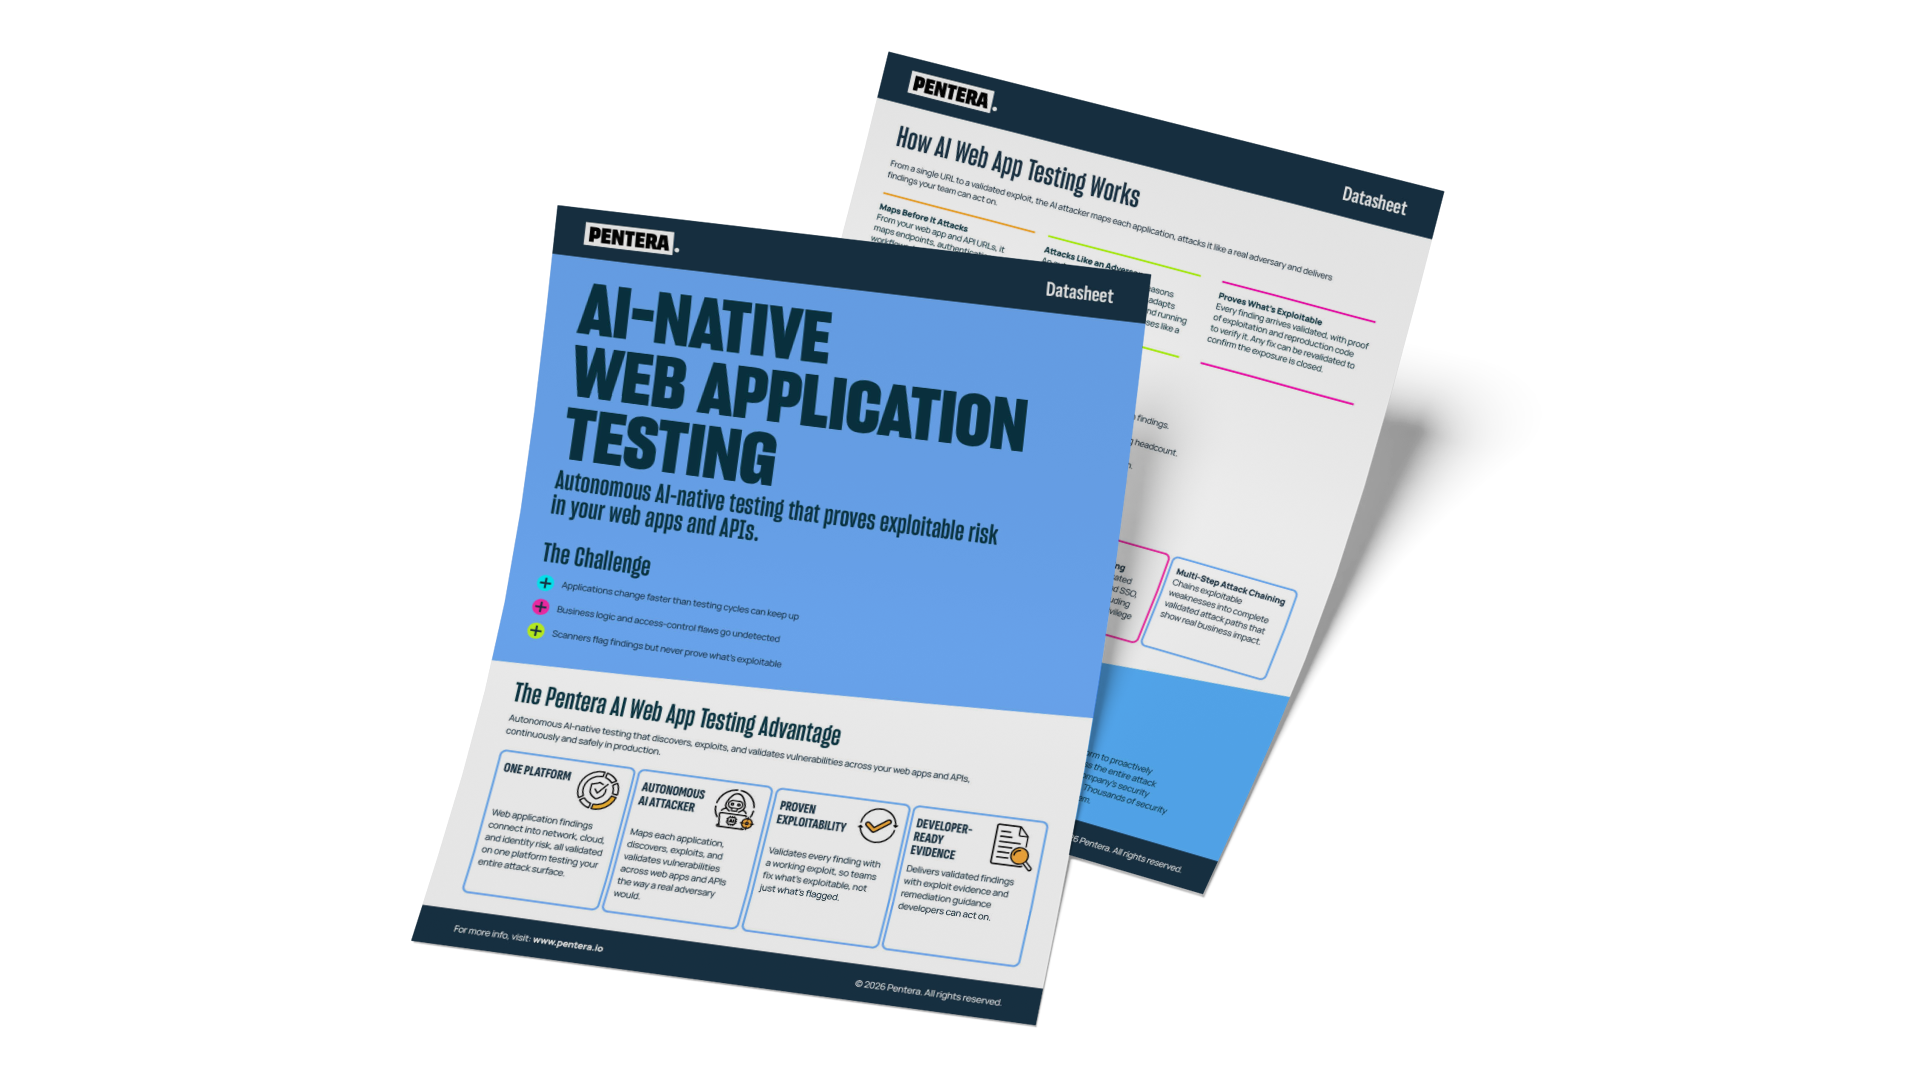
Map applications, reason through logic, adapt payloads in real time, and chain weaknesses into complete attack paths. Results are deterministic, reproducible, and auditable.
Cut through scanner noise and alert fatigue. Confirm every finding with evidence. Prioritize remediation of proven risk, not potential flags.
Test continuously as your applications and APIs evolve, without adding headcount or waiting for the next manual pentest.
Chain application flaws through your network, cloud, and identity to see the complete attack path.
Equip developers with proof of exploitation and remediation steps. Retest to confirm fixes are closed.
Autonomous web app testing harnesses AI through customer-defined boundaries. Every action is governed by architectural controls, not prompt-level filters. Deterministic execution ensures every test is controlled, repeatable, and auditable. No maintenance windows, proven across 1,300+ customer environments over 10 years.
Enter one or more web application or API URLs to begin testing.
Set the permitted targets, access permissions, and safety guardrails. Add credentials, tokens, or session details for testing behind SSO, MFA, and OAuth.
The AI attacker maps the application, reasons through its logic, adapts payloads, and chains exploitable weaknesses to demonstrate their impact.
Generate executive and technical reports that communicate proven risk, business impact, and remediation progress.
AI web application testing is dynamic, attacker-led testing that maps an application’s endpoints, authentication, workflows, and logic, then selects and adapts attack techniques in real time. Deterministic tools confirm the result, so every finding is backed by evidence rather than an AI assumption. It is not static source-code analysis, and it is not a vulnerability scanner.
Yes. The OWASP Top 10 is the baseline, not the limit of Pentera’s testing. Pentera’s AI Web Application pentesting goes beyond known vulnerability patterns to reason through application logic, authenticated workflows, and access controls, adapting its attacks to uncover and prove exploitable risk that standardized testing can miss.
Vulnerability scanners flag potential weaknesses by signature and leave your team to determine which are real. Pentera instead acts like an attacker, discovering exposed applications, gaining authenticated access, chaining flaws together, and safely proving exploitation with evidence your team can act on.
Pentera combines AI-driven reasoning with deterministic validation to produce controlled, repeatable, and auditable results. It also connects web application findings to network, cloud, and identity on the same platform, allowing teams to understand risk beyond the application itself.
Yes. AI-Native Web Application Testing runs within customer-defined targets, access, and guardrails, with a complete audit trail of every action. Testing remains bound to the scope you approve.
Yes. Where an attack path continues beyond the application, so does Pentera, extending from the application into infrastructure, cloud, and identity within the scope you define. This shows the full path an adversary could take, not just the initial application flaw.
No. DAST and scanners flag potential weaknesses by signature; Pentera executes real attacks and validates exploitability with proof. SAST finds code issues early but cannot prove runtime exploitability; Pentera catches logic flaws and access control issues SAST misses. Manual pentesting applies deep reasoning but runs point-in-time; Pentera runs continuously, combining pentest-level depth with modern release frequency. Where scanners produce noise, Pentera produces proof.